Drive by Downloads
Drive-by downloads automatically install malware when users visit compromised websites, often without any user interaction or consent. These attacks silently download malicious files on victims' systems. Tax scam campaigns frequently use this technique, targeting users during tax season with fake tax preparation websites that automatically deliver malware designed to steal financial information, credentials, and personal data.
Defend With SquareX
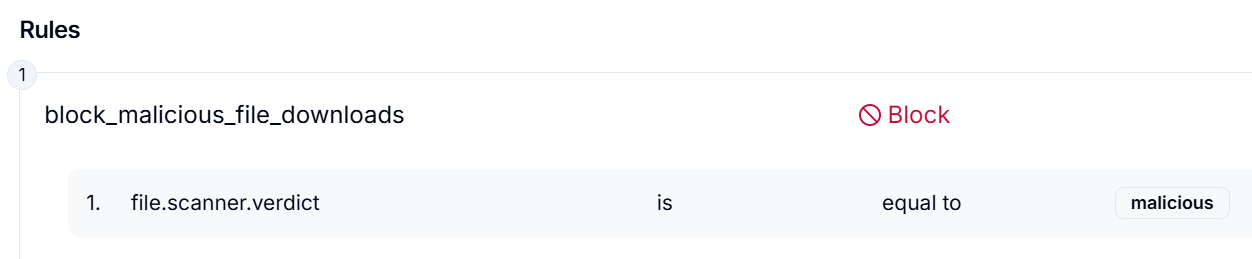
Create a file download policy to Block malicious file downloads.
Example Policy
Follow These Steps
- Click on Launch Attack Simulation button
- With SQRX enabled, file download will get blocked.
Details
Suspicious or malicious files delivered through drive-by downloads automatically install malware on users’ systems when they visit compromised websites, typically without any user interaction. File type inspection helps identify and block these harmful files before they can execute. Drive-by downloads are commonly used in tax scam campaigns, where fake tax preparation sites silently deliver malware to steal financial data, credentials, and personal information.
Impact
Victims of drive-by downloads often suffer from malware infections that can lead to stolen sensitive data, identity theft, financial loss, and unauthorized system control. These attacks damage user trust and privacy while causing potential disruption to personal or business computer systems.
Indicator of Compromise (IOC)
- Unexpected file downloads or installations without user consent.
- Detection of anomalous or suspicious file types during file inspections.
- Network traffic to known malicious or compromised websites often related to tax scams.
- Presence of malware signatures or unusual system behaviors following visits to suspicious sites.