Allow Specific Extension
Unvetted browser extensions pose significant security risks as they can access all browsing data, modify web pages, steal credentials, and inject malicious code. Whitelisting specific vetted extensions ensures only authorized, security-reviewed tools are installed, preventing unauthorized data access and browser-based attacks.
Defend With SquareX
Create a browser extension policy to Allow specific extension.
Affected Companies:
Cyberhaven
Internxt Vpn
Vpncity
Example Policy
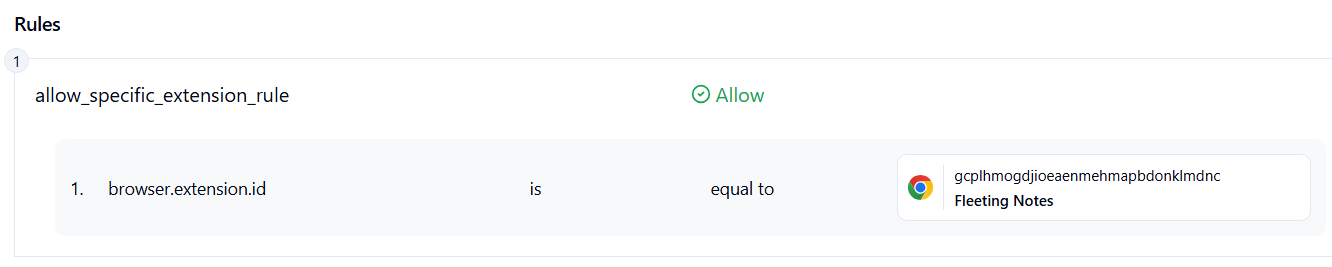
Follow These Steps
- Install any extension from Extension store
- Extension will get blocked by Squarex
- Click on Launch Attack Simulation button
- Fleeting notes extension will not get blocked
Details
Malicious browser extensions represent a significant threat vector where cybercriminals develop seemingly legitimate browser add-ons that contain hidden malicious functionality designed to steal sensitive data, monitor user behavior, inject malicious content, and compromise system security. These extensions are distributed through official browser stores (Chrome Web Store, Firefox Add-ons, Microsoft Edge Add-ons) exploiting users' trust in legitimate platforms.
Malicious extensions exploit permission models where extension modifies web pages to steal form data and session cookies, background script execution that continuously monitors user activity and network traffic, dynamic code loading that downloads additional malicious payloads after installation, DOM manipulation to inject fake login forms or redirect users to phishing sites, and command and control communications through encrypted channels to receive instructions and exfiltrate stolen data.
Impact
Credential Harvesting: Extensions can monitor form inputs, keystrokes, and autofill data to capture usernames, passwords, credit card information, and authentication tokens across all visited websites.
Session Token Theft: Malicious extensions can extract authentication cookies, JWT tokens, OAuth tokens, and session storage data, enabling account takeover attacks without needing user credentials.
Financial Data Exfiltration: Extensions specifically target banking websites, cryptocurrency exchanges, and e-commerce platforms to steal financial information, transaction details, and payment credentials
Ad Fraud and Click Injection: Extensions manipulate web pages to inject malicious advertisements, redirect affiliate links, or generate fraudulent clicks for financial gain.
Indicator of Compromise (IOC)
Extension Behaviors: Excessive permissions requests, sudden functionality changes, obfuscated JavaScript code.
Artifacts: Unauthorized files in extension directories, modified browser preferences, suspicious registry entries for non-store extensions
Performance Issues: High browser CPU/memory usage, connections to crypto mining pools, unexpected disk activity, frequent browser crashes.
Authentication Issues: Simultaneous logins from multiple locations, stolen session tokens, MFA bypass attempts, mass password reset requests