Block Phishing Sites
Attackers use phishing login pages to instantly capture usernames and passwords, gaining immediate access to victim accounts across email, banking, social media, and corporate systems.
Defend With SquareX
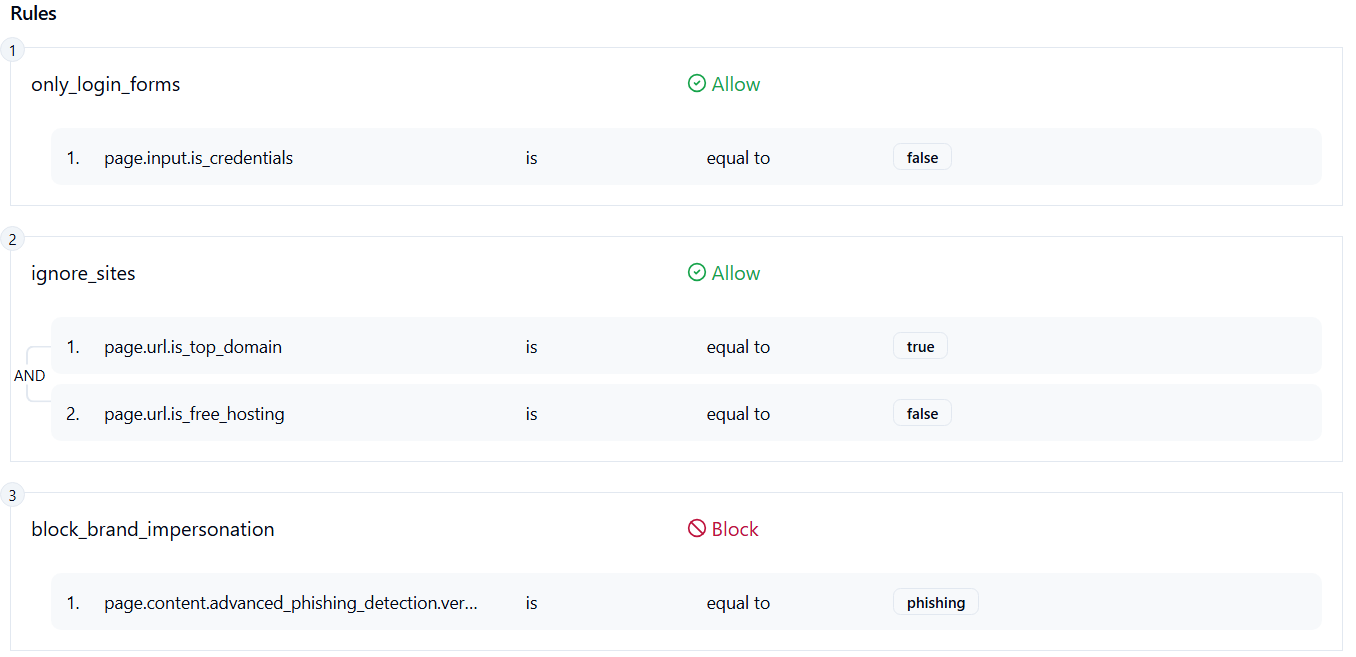
Create a user input policy to Block phishing sites.
Affected Companies:
Mgm Resorts
Fcc
Microsoft
Example Policy
Follow These Steps
- Click on Launch Attack Simulation button
- With SQRX enabled, webpage will be blocked
Details
Cybercriminals create sophisticated phishing websites that precisely mimic legitimate login pages to capture usernames and passwords in real-time, providing immediate access to victim accounts across email services, banking platforms, social media networks, and corporate systems. These phishing sites utilize advanced techniques including pixel-perfect cloning of legitimate websites with identical visual elements, real-time credential harvesting that instantly transmits stolen data to attacker-controlled servers, adaptive content delivery that serves different phishing pages based on victim characteristics or referral sources, and social engineering elements that create urgency or fear to pressure victims into entering credentials.
Impact
Immediate Account Compromise: Successful phishing attacks provide attackers instant access to victim accounts, enabling immediate unauthorized actions including email access, financial transactions, data theft, and account modifications before victims realize their credentials have been compromised.
Corporate Network Infiltration: Employee credentials harvested through phishing provide attackers direct access to corporate email systems, cloud applications, and internal networks, enabling data breaches, intellectual property theft, and lateral movement throughout organizational infrastructure.
Identity Theft and Social Engineering: Compromised email and social media accounts enable attackers to impersonate victims for business email compromise schemes and targeted social engineering attacks against the victim's contacts and business associates.
Indicator of Compromise (IOC)
Page Content Analysis: Websites containing exact replicas of legitimate login forms with identical field names, styling, and JavaScript functions, pages using stolen logos, images, and branding materials from legitimate companies without authorization.
Form Submission Behavior: Login forms that submit credentials to external domains different from the displayed website.
URL and Domain Characteristics: Websites using slight variations of legitimate domain names through character substitution or addition, sites hosted on suspicious domains with recent registration dates